What did an agent do?
Visibility
Follow recorded activity, see who’s responsible, and focus on work that needs attention.
Scopebond brings visibility, control, and evidence together for your connected AI coding tools. See what agents do, block supported harmful actions, and share records others can check.
As AI adoption grows, your organization needs a clear view of its actions, protections, and evidence.
Follow recorded activity, see who’s responsible, and focus on work that needs attention.
Apply your rules to stop supported harmful actions before they run. Review rule changes with your team.
Share signed records of actions, rules, and decisions that reviewers can check independently.
A shared workspace connects recorded activity, responsible people, rules, and evidence—so oversight becomes part of everyday work.
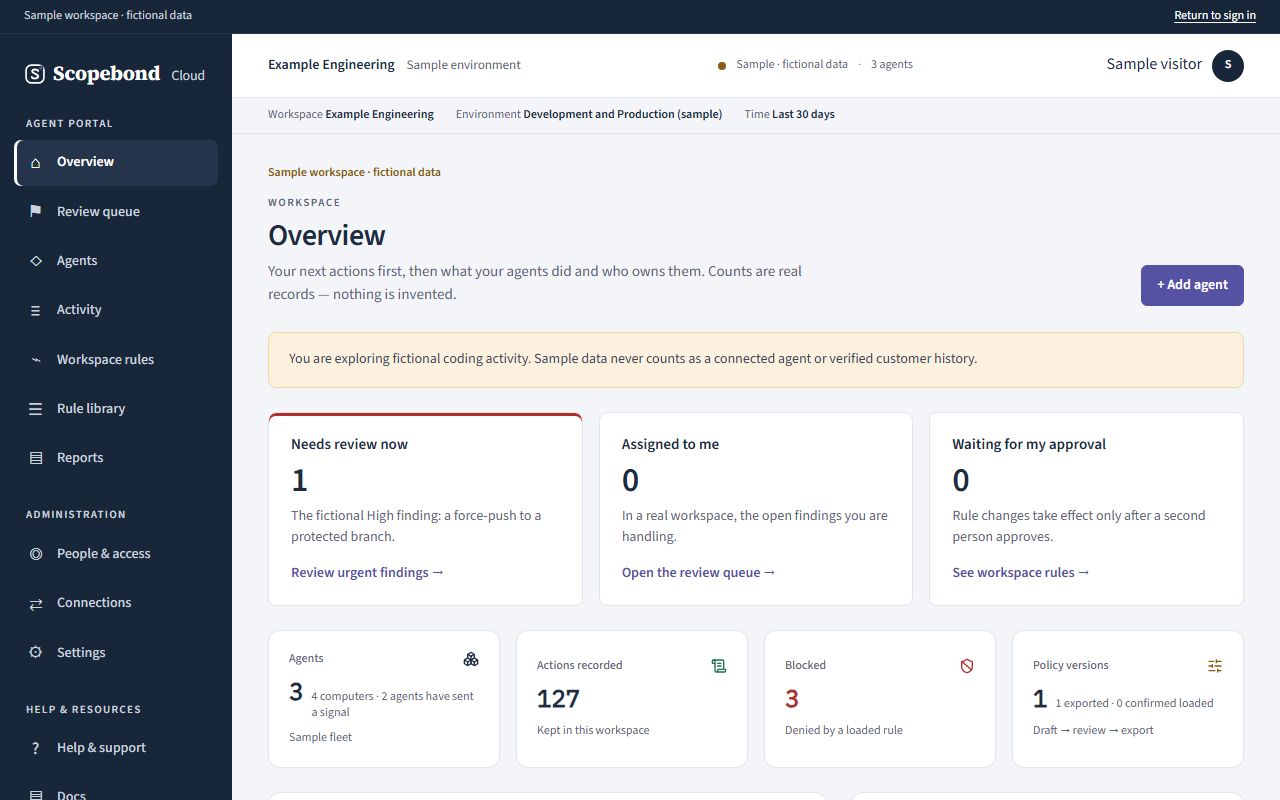
Understand the requested action and the agent responsible.
The supported action is stopped before it runs.
A signed record connects the action, rule, and decision.
This illustrative sample is signed with the published sample key. It is not customer history; its signature does not independently prove an external outcome.
{
  "type": "scopebond:receipt",
  "realtime_result": "deny",
  "executed": false,
  "intent": {
    "action_type": "git.push",
    "params": {
      "remote": "origin",
      "ref": "main",
      "force": true
    }
  },
  "policy_ref": {
    "id": "coding-agent-starter",
    "version": 1,
    "digest": "b660a1b81fcac7a688c760b9df347463d3256163d08b9bdd4b6f39981955f509"
  },
  "execution": {
    "state": "denied",
    "external_effect": "not_independently_verified"
  },
  "attester": {
    "kind": "gateway",
    "kid": "key:352d5e1592d02d3b"
  },
  "timestamp": "2026-09-21T14:14:07Z"
}Illustrative protected-branch example. Coverage depends on the configured connection.
See how it worksSupported actions can be checked before execution or merge. Some actions are recorded for review rather than prevented.
Explore integrations and coverageUnderstand what Scopebond protects, how setup works, and what you can demonstrate.
Review trust and securitySupported actions routed through a configured connection that break your rules. GitHub checks must be required to prevent merging. Actions outside the connection are not covered.
A developer connects your supported tools. Owners and reviewers can then use the workspace to follow activity, review rules, and share evidence.
The recorded action request, rule, and decision. Reviewers can check signatures independently. A signature alone does not establish an external outcome or compliance.
Activity records are designed to exclude prompts, file contents, and secrets. The Trust and Privacy pages explain the data Scopebond holds.
On connected computers or in your own workflow. The shared workspace brings activity, rule review, and evidence together.
Bring visibility, control, and evidence into your organization’s AI oversight.